etcd node ×3
- vCPU
- 2
- Memory
- 4 GB
- Disk
- 50 GB SSD
Kubernetes, GitOps, observability and zero-trust security, plus the Ruckos developer tools, on any enterprise hardware, in your datacenter.
Cloud-native development allows your organization to build and run apps engineered to take advantage of cloud computing. Using modern architectures, technologies, and practices, teams can quickly ship cloud-native applications, update them as fast as customer needs change, and scale them on demand. Delivered with high availability and security, cloud-native systems operate in a variety of computing environments, including public, private, and hybrid clouds and on-premises infrastructure.
It's been a barrier for some organizations that don't have the expertise or resources to manage the complexities of hosting Kubernetes. We aim to simplify the process and provide a platform that allows organizations to focus on building and deploying their applications without worrying about the underlying infrastructure. Our platform is designed to be user-friendly, scalable, and secure, making it easier for teams to adopt cloud-native practices and take advantage of the benefits of cloud computing.
Boot Ruckos Linux on bare metal, Ruckos Virtualization or Hyper-V, and it becomes a running Kubernetes cluster with GitOps, observability and security already installed. Developers self-serve from the portal.
Ruckos automation bootstraps a private cloud and installs the platform services.
Create nodes and clusters, deploy from Git, and keep every cluster matching what's declared, from rctl or the Lighthouse web console.
A container management and deployment engine built to give teams real control over the cluster. It doesn’t just scale — it gives you continuous visibility into exactly what is installed and running, monitored through GitOps so the live state always matches what’s declared in Git.
Fleet state stays declarative, visible, and reversible.Deploy from Git using raw Kubernetes YAML, Helm charts, Kustomize, or any mix of the three. Every source is normalised into a Helm release and deployed through a single, consistent engine — giving you control, repeatability, and a full audit trail across every cluster.
Every path lands in the same repeatable delivery system.Define policies and configuration once, then apply them across multiple clusters. Drift is detected and the live state reconciled back to Git, so you can be confident that every cluster is running exactly what you expect.
Policy and environment changes propagate without configuration sprawl.
A single root Application points at your cluster's folder in the gitops repo. From there ArgoCD owns everything — platform services, projects, and workloads all unfold declaratively.
Per-cluster folders scaffolded from a template, never overwrittenAn opinionated, fixed set of services installed the same way on every cluster: cert-manager, an in-cluster registry, Keycloak, Grafana, Loki, and Tetragon — all governed by ArgoCD AppProjects.
Identical, drift-free deployments across every environmentAppProjects for dev, qa, prod, sandbox, and platform fence what each tier may deploy — sandbox is restricted to its own namespaces and a whitelist of resource kinds.
Least-privilege boundaries enforced by ArgoCD, not conventionDevelopers provision workloads through a catalog. The platform renders manifests and commits them to git; ArgoCD detects the new path and syncs it live.
Provision → commit → sync → live, with git always authoritativeFour small tools take a developer from nothing to a running service, or bring an existing project across.
Self-service catalog that provisions databases, caches and starter projects into each developer's own namespace. Sign-in is single sign-on through Keycloak, brokered to Active Directory.
Starter projects come prebuilt and open straight in VS Code through short-lived git-drop repos that expire on their own.
Scans a repo, builds a profile, validates it and renders Kubernetes manifests for dev, qa or prod, ready for GitOps.
Moves a developer's Azure DevOps repositories to GitHub: clones them, creates and fills the new repos, and records the app's owner and details.
Each tool is a container. It runs on Kubernetes, or natively on Ruckos Linux as a Ruckos Microservice.
Ruckos Platform makes it easy for developers and engineers to securely build and deploy containerized applications no matter what your devops or gitops experience is. We obscure all of the complexities so you can spend more time in the IDE.
The CLI tool seamlessly integrates with established CI/CD pipelines.
Our powerful UI and CLI help you build complex workloads at scale, giving you easy access to your Kubernetes environments, hosts, stacks, services, and containers.
When cluster deployment and management is automated and immutable across clouds, on-prem, and the edge, developers can focus on writing code that delivers differentiating services — not the infrastructure that runs them.
Customize and extend the Ruckos platform to fit specific use cases and development requirements with our extension catalog and integrations library.
Prometheus scrapes every workload and node; Grafana ships pre-loaded with dashboards for cluster health, GitOps sync status, and resource usage.
Loki aggregates logs across every namespace and cluster so you can search and correlate without shipping data off-platform.
Tetragon watches process execution, network flows, and file access at the kernel level, giving you security observability without sidecars or agents.
Alert rules ship with the platform and route through Grafana, so you know about a failed sync or a struggling pod before your users do.
RBAC is enforced at the API level, network policy is enforced at the kernel level, and every workload certificate is issued and rotated automatically.
Tetragon enforces process, network, and file-access policy at the kernel level in real time — not just logging violations after the fact.
Cilium enforces network policy and encrypts pod-to-pod traffic with eBPF — no service mesh, no sidecars, no added latency.
cert-manager issues and rotates every workload certificate from your own CA — no manual renewals, no expired certs taking down production.
No SSH, no systemd, no package managers on nodes. A read-only root filesystem means nothing to patch and nowhere for an attacker to persist.
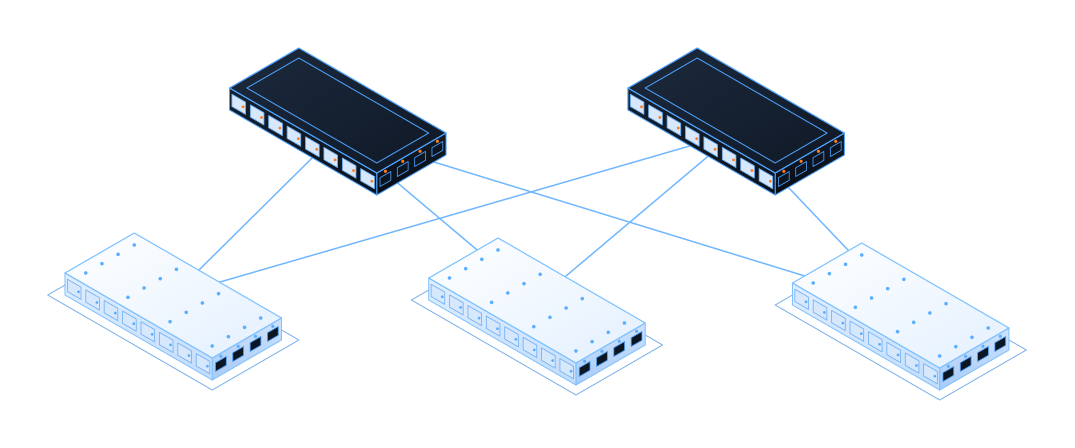
Cilium is the only networking layer on the cluster. It routes pods, replaces kube-proxy, terminates Gateway API traffic, and enforces identity-based network policy — all from eBPF programs attached to the datapath.
Hubble reads flow data straight from Cilium's eBPF datapath. Every connection, DNS lookup, HTTP request, and policy drop is visible with the pod identity attached — without a packet capture or a sidecar.
Tetragon attaches eBPF programs to process, file, and network syscalls. It can observe them, or it can kill the process in the kernel before the syscall returns. The agent that marries those events to Kubernetes metadata runs once per node, not once per pod.
The platform allows operations teams to focus on infrastructure and developers to write code, Ruckos Platform helps you bring products to market faster and accelerate your organization's digital transformation.
Private clouds are adapting to support Microservices and local LLMs. By using technology that simplifies how services and apps are packaged and managed, businesses can develop and launch software more efficiently across private, hybrid, and Azure clouds — making it easier to integrate new technologies, streamline workflows, and respond to changing business needs.
With Ruckos Linux, organizations can reduce or eliminate the need for costly VMware licensing, optimizing their IT budgets.
With Ruckos Linux, organizations can reduce or eliminate virtual machine maintenance, patching, and associated costs, streamlining IT operations.
When organizations need full control over their infrastructure, single-tenant deployments are ideal. These setups are owned or dedicated entirely to one organization and can be hosted on-premises or off-premises.
Ruckos Hybrid Cloud allows organizations to extend their on-premises infrastructure into Microsoft Azure, enabling them to leverage the scalability and flexibility of the cloud while maintaining control over their data and applications. This hybrid approach provides the best of both worlds, allowing businesses to optimize their IT resources and respond quickly to changing demands.
 Ruckos Cloud
Stand up an encrypted Site-to-Site VPN in minutes, or step up to a private ExpressRoute circuit for dedicated bandwidth and predictable latency that never touches the public internet.
Extend Ruckos onto Azure's NC- and ND-series GPU virtual machines for on-demand training and inference capacity, without buying, racking, or cooling GPU hardware yourself.
Point pipelines at Azure Databricks and other managed data services that were never meant to run on-prem, while Ruckos keeps compute, orchestration, and control on infrastructure you own.